Traditional defenses struggle against modern threats
Don’t wait for attacks. Be preemptive.
Recent research shows a sharp rise in A.I. and bot attacks, costing companies ~$5M per incident. Observable zero-day attacks have increased ~42%, while the fastest infiltration times have dropped ~65% — now as quick as 27 seconds.
The solution: a global preemptive cyberdefense grid
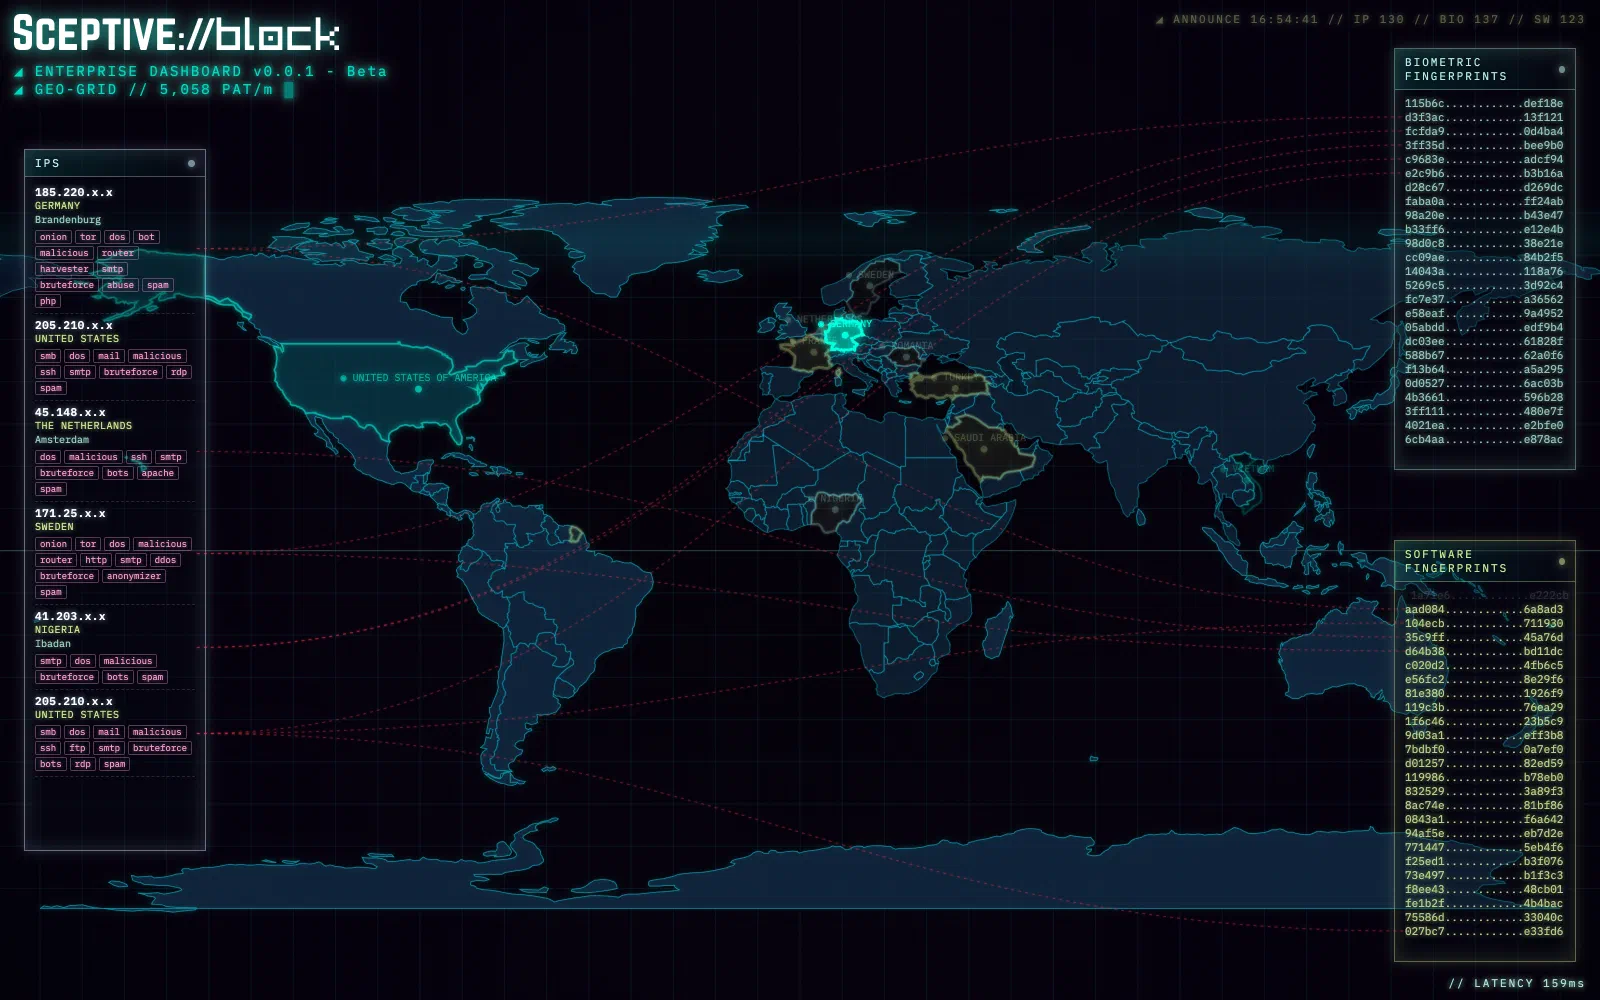
operates as an expansive, worldwide cyberdefense grid that identifies and evaluates cyber threats in real time. By delivering direct signals to your firewalls, it safeguards your infrastructure and halts attacks at the most efficient, frictionless perimeter.
| Grid at a glance | |
|---|---|
| IP addresses in the grid database | 7.5+ million |
| Hackers actively tracked worldwide | 12,000+ |
| Persistent advanced threat sources processed | ~5,000 every minute |
How it works: multilayer threat fingerprinting
- Fingerprint global adversaries. Through the deployment of diverse fingerprinting methods, including behaviour biometric analytics, monitors global adversaries. This allows persistent tracking of malicious actors even as they rotate their hardware, geographic positions or IP addresses.
- Signal your firewalls. Threat sources are prioritized based on attack vector technique and sophistication, then converted into actionable signals pulled directly by firewalls. As a result, global attacks are automatically thwarted at the perimeter of corporate networks.
To monitor in real time how runs globally, visit world.block.sceptive.com.
High ROI: infrastructure relief through silent edge drops
By neutralizing threats at the perimeter, internal resources — including application servers, WAFs, IDS and SIEM platforms — experience significant operational relief.
Without bl0ck, malicious requests consume compute cycles and trigger endless security alerts. With bl0ck, silent drops at the firewall level ensure your internal stack only processes legitimate traffic.
Integration and activation: faster than reading this page
Activating on your infrastructure is as easy as possible:
- Register a corporate account at block.sceptive.com.
- Activate your API subscription.
- Configure your firewall in minutes — your infrastructure shield is up instantly.
Works with F5, Check Point, Cisco, MikroTik, Sophos, Fortinet, Palo Alto and any firewall that can consume a plain list.
There are no maintenance payments or integration services, and no hidden costs.
Customer success: 3.47 million attacks blocked in 3 days
At this very moment, is actively safeguarding millions of people worldwide. It currently neutralizes approximately 1 million attacks daily for a telecommunications client in Eastern Europe, providing robust protection against global threats as you read this page.